ISO/IEC 27001:2022 Lead Implementer · ISMS training · self-paced

Build an ISO 27001 ISMS from your real risks. Scope it, score the risk, justify each control.

Learn ISO/IEC 27001:2022 in the order you'd build it: scope, risk method, Statement of Applicability, controls across all four Annex A themes, internal audit, management review and the certification audit. You draft each piece for your own organization, with Coach Q beside you.

For ISMS leads, IT and security managers, and quality or compliance managers whose customers ask for ISO 27001, building a first ISMS or fixing one.

Start free. Lesson 1, with Coach Q, no card.

A customer questionnaire asks if you are ISO 27001 certified. Audit the answer and build a business case a CEO can sign.

See everything you get ↓ Lessons for life · coach included, no renewal fee
  • About 9 hours
  • Self-paced
  • Private AI coach
  • Certificate of completion
academy.qmslearning.com
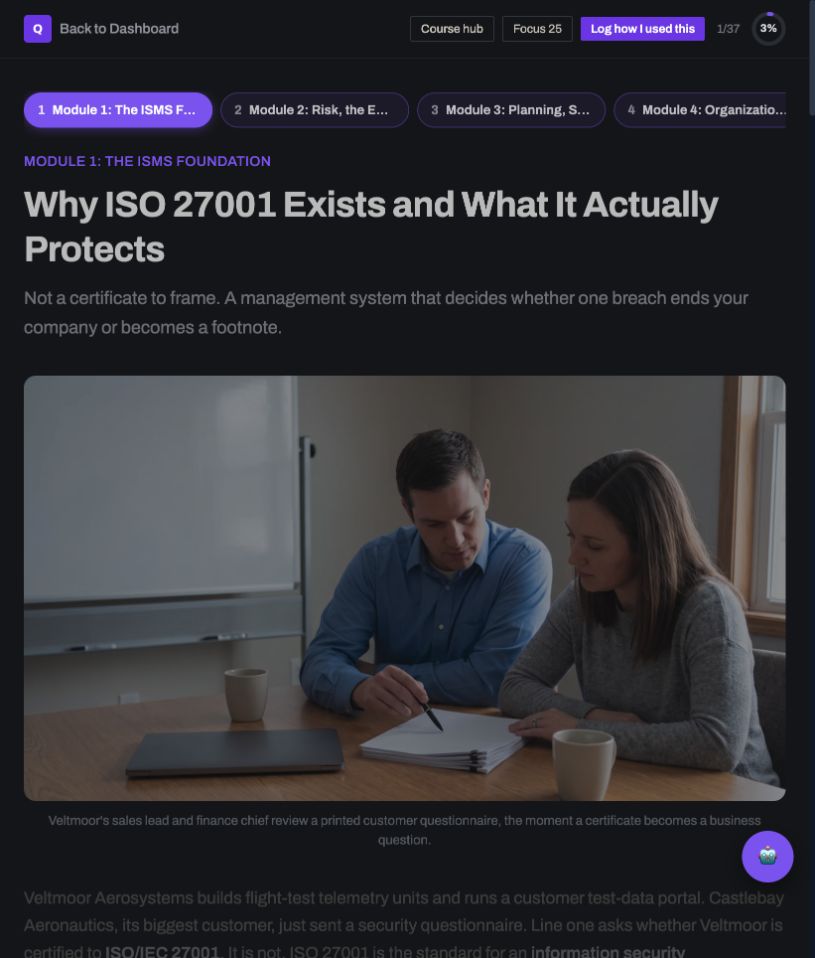
Lesson 1 of ISO 27001 Lead Implementer, a real screen from the course

Can we just mark all 93 controls implemented?

COACH Q · IN YOUR POCKET

No. Build the SoA from your risk treatment, then cross-check Annex A. A checkmark you can't back up invites the first question.

Real screen from this courseLesson 1 is free

Sound familiar?

You'll hear these before your first ISO 27001 audit.

A customer asked if we're ISO 27001 certified.

And the honest answer was no. Buyers ask because they can't see inside your operation, and following ISO 27001 isn't the same as being certified. You'll learn what the certificate actually proves and build the business case your CEO or CFO needs to fund it.

Our template has 114 controls.

Then it was written for the 2013 edition, and the transition to 2022 closed October 31, 2025. The 2022 Annex A has 93 controls in four themes. You'll learn the thirty-second check that catches old material before you build on it.

Every risk on our register is High.

Sixty urgent risks means nothing is prioritized, so the cheap ones get fixed and the dangerous one waits. You'll set scales and criteria that rank risk on evidence, not dread, and give each risk a named owner, never a department.

Just have AI write the Statement of Applicability.

It will. It may also mark all 93 controls applicable and implemented, the way a downloaded template does, and every 'implemented' is a promise of evidence. You'll build the SoA from your own risk treatment, with a reason for every control you exclude.

What it does for you

Be the one who can answer “Are you ISO 27001 certified?”

A seat in the sales conversation

Security questionnaires can decide who wins the work. The person who can answer them honestly, and build the system behind the answer, becomes part of how the company wins.

An ISMS with your name on it

Scope, risk method, Statement of Applicability, internal audit and management review, prepared for your own organization.

Proof on your record

A certificate of completion anyone can verify, for your training record and your LinkedIn.

No course can promise you a raise or a title. What you'll have is the skill, the work to show for it and a certificate anyone can verify. That's what those conversations run on.

Why it matters

Why customers ask their suppliers about ISO 27001.

$4.99M

IBM and Ponemon Institute's Cost of a Data Breach Report 2026 puts the global average cost of a data breach at $4.99M, up 12% over the previous year and a record high.

Source: IBM and Ponemon Institute, Cost of a Data Breach Report 2026

When you hold a customer's data, your breach is their problem too, and they can't see inside your operation. So their security questionnaire asks whether you're ISO 27001 certified. The certificate is an independent body telling them you run a managed system for their data. That's why it shows up in procurement.

An ISMS won't make you unbreachable. It decides whether a breach is a catastrophe or a managed event: you know what data lived where, someone has the authority to act tonight, and the customer notice duties are already on file. That's the system an auditor tests, and the one you build here.

What you'll learn

Every clause and control, in the order you'd build it.

Seven modules take you from a customer's questionnaire to the certification audit. Every lesson works a case at Veltmoor Aerosystems, a fictional maker of flight-test telemetry units, then has you draft the same piece for your own organization.

01Module 1 · Clauses 4 and 5

Make the business case, then draw the scope

It starts with a customer questionnaire asking if you're certified. You learn what a certificate proves, then set context, interested parties and a scope that follows the data, a policy top management can explain, roles with real authority, and the check that spots a 2013 template.

  • A business case: revenue at risk and revenue you could win, kept apart, each cost owned
  • A 4.3 scope that names the cloud host and the supplier with admin access as interfaces
  • 5.3 roles with the authority to act, and A.5.3: nobody approves their own access

02Module 2 · Clause 6.1.2

Build a risk method that gives the same answer twice

Clause 6.1.2 wants results that are consistent, valid and comparable every time. You write likelihood and consequence scales in units your business measures and set acceptance criteria before you score anything. Then you identify risks by loss of confidentiality, integrity and availability, each with a named owner.

  • Two assessors score the same scenario. More than a band apart, you investigate
  • Three questions per flow: who shouldn't see it, what if it's wrong, what if it's down
  • Likelihood scored from your own records, like exit logs, never from comfort or dread

03Module 2 · Clause 6.1.3

Treat the risk and write the Statement of Applicability

Annex A is a cross-check, not a shopping list. You pick treatment options, determine controls from any source, compare them with Annex A so nothing needed is missed, and get each risk owner's written approval of the plan and acceptance of the residual risk. The SoA falls out of those decisions.

  • Treatment options from ISO/IEC 27005 guidance: avoid, modify, share or retain
  • SoA lines with a risk reference, an honest status (planned counts) and a dated record
  • A reason for every Annex A control you exclude. Exclusion is allowed. Silence isn't.

04Module 3 · Clauses 6.2 to 8

Run it: objectives, change, people and documents

Clause 8 is where the ISMS stops being a document and becomes something you run. You set objectives with a number, a date and a name, plan changes under 6.3, prove competence and awareness, and keep one current version of every controlled document.

  • Clause 6.3, new in 2022: a change request dated after the cutover proves it wasn't planned
  • 7.2 competence evidence that isn't an opinion or checked by the person it describes
  • 8.2 risk reassessment at planned intervals and whenever a significant change is proposed

05Modules 4 to 6 · Annex A

Put all 93 controls to work across four themes

All 37 organizational, 8 people, 14 physical and 34 technological controls, taught through decisions you'd face on the job. You'll handle the account that should have been gone, drawings a supplier wants by email, a breached server you're tempted to rebuild before the weekend, and a backup nobody has restored.

  • A.5.18: check accounts against HR and supplier notices, or the review can't find leavers
  • A.5.28: isolate, image the disk, keep the logs, then rebuild. Evidence comes first
  • A.8.13: a Success status isn't a restore. A failed one gets a nonconformity and a retest

06Module 7 · Clauses 9 and 10

Audit it yourself, then face Stage 1 and Stage 2

Find the gap before the certification body does. You plan a risk-weighted internal audit programme where nobody audits their own work, run a management review that ends in decisions with owners and dates, fix causes instead of symptoms, and learn what Stage 1 and Stage 2 each test.

  • 9.2.2 impartiality: cross-assign, use another function or an external internal auditor
  • All seven 9.3.2 review inputs, including interested parties' needs, separate since 2022
  • Stage 1 reviews documents and readiness. Stage 2 samples records, traces risk to control

Who built it

Written by a registrar auditor whose own company holds ISO 27001.

Will Trikha

Founder and CEO, QMS Learning · Third-party registrar auditor

Will Trikha is a third-party registrar auditor with more than 20 years in aerospace and quality. He wrote this course from ISO/IEC 27001:2022, clause by clause and control by control, around the evidence an auditor asks to see: the dated record behind each 'implemented', the owner's signature on each accepted risk.

His own company, QMS Learning, earned ISO 27001 certification in 2026. The scope statement, risk method, Statement of Applicability, internal audit and management review you build here are the documents a certification audit asks for. As COO of PTX Defense, an AS9100D-certified aerospace manufacturer, he also sees customer security requirements from the supplier's side.

What a certification auditor pulls on first

  1. Whether the scope covers what the customer askedA scope that excludes the cloud tenancy the system runs on contradicts itself. Clause 4.3 asks you to consider interfaces and dependencies, so a supplier with remote admin access is named on the boundary, not waved outside it.
  2. The evidence behind every 'implemented'Each applicable line in the Statement of Applicability is a promise of evidence. The auditor picks one and asks for the record, like a dated restore test. Planned, with a target date, is an honest status. Implemented with nothing behind it is a finding.
  3. A signature on every accepted riskClause 6.1.3 f) needs the risk owner to approve the treatment plan and accept the residual risk. A hallway 'we can live with that' is a decision with no owner. The owner is a named person with authority, never a department.
  4. Dates that fight each otherEvidence dated after the SoA that claims it. A target date that falls before the plan was written. Minutes approved before the meeting was held. Any one of them undermines the whole document.

Check us before you pay

  • Take lesson 1 free. The real first lesson with Coach Q. No card.
  • Look Will up. His LinkedIn profile lists the work behind the course.
  • Check a certificate. Every certificate can be confirmed at academy.qmslearning.com/verify.
  • Keep your exit. 3 days after you buy to ask for a refund.

The usual way, and this course

A template gives you words. The auditor tests them.

The usual route starts from a filled-in template. This course starts from your scope and your risks, the way the standard reads.

The usual way
This course
Where you start
A template with all 93 controls already marked applicable
Your scope and your risks, then the controls they call for
Scoring risk
A workshop on gut feel, where nearly everything ends up High
Defined scales and criteria, so two assessors land on the same score
Before the audit
Learn at Stage 1 what the auditor expected to see
Your own internal audit, management review and Stage 1 readiness pack first
How it fits you
The same pace and the same examples for everyone
A study plan sized to your week, and a coach that works on your own job
When you're stuck
Email the instructor and wait for a reply
Ask Coach Q on any screen, any hour
After you finish
Access often ends after a year
Lessons for life, kept up to date, and a coach that stays with you

Not like training used to be

Short, hands-on, built around you. And the coach stays.

Training used to mean days in a classroom or hours of video. Here are real screens from ISO 27001 Lead Implementer: short sessions where you make the call, a plan that fits your week, and an expert in your pocket.

Coach Q · your expert on call

A prospect wants our Statement of Applicability. Can we just mark all 93 controls implemented?
COACH Q

No. The SoA records the controls you need, why you need each one, whether each is implemented, and why you excluded any Annex A control (Clause 6.1.3 d). Marking everything implemented invites the first question you can't evidence.

Build it from your risk treatment first, then cross-check Annex A so nothing relevant is missed. A one-line reason for excluding a control that covers an activity you don't perform is stronger than a checkmark you can't back up.

Coaching, not decisions. You make the call. Comes with your course, no renewal fee.

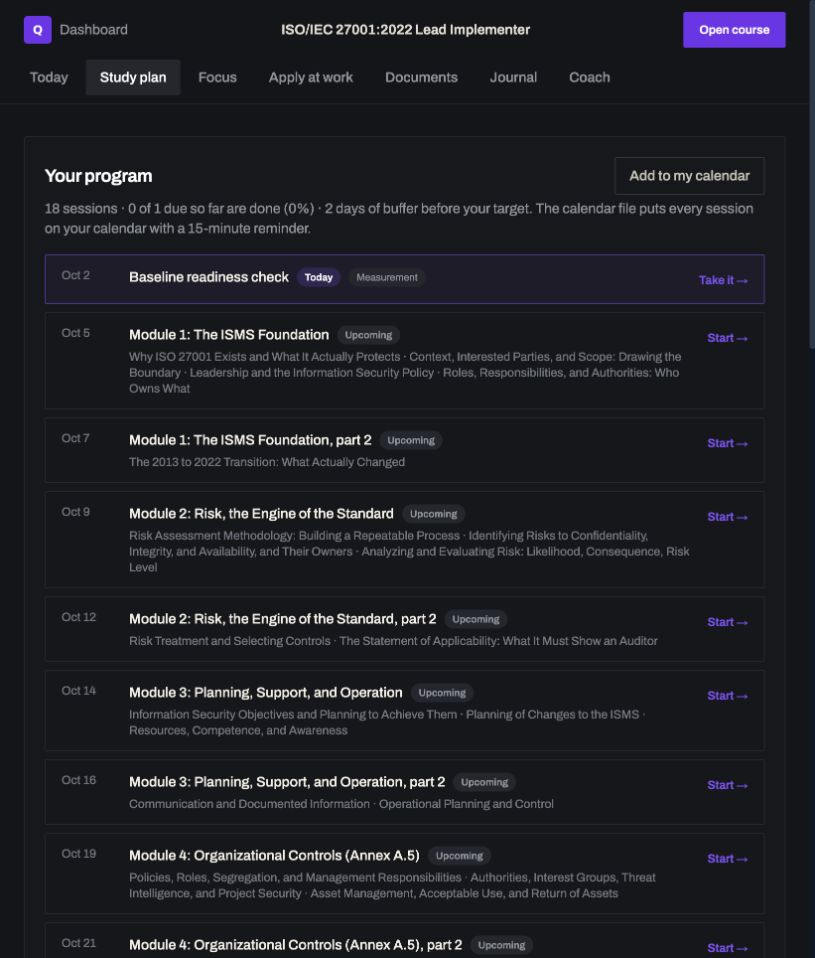
Study plan: a real screen from ISO 27001 Lead Implementer

Study plan · Your personal trainer

Tell it your goal date. It builds sessions around your week and shows each day whether you're on plan, so the course actually gets finished.

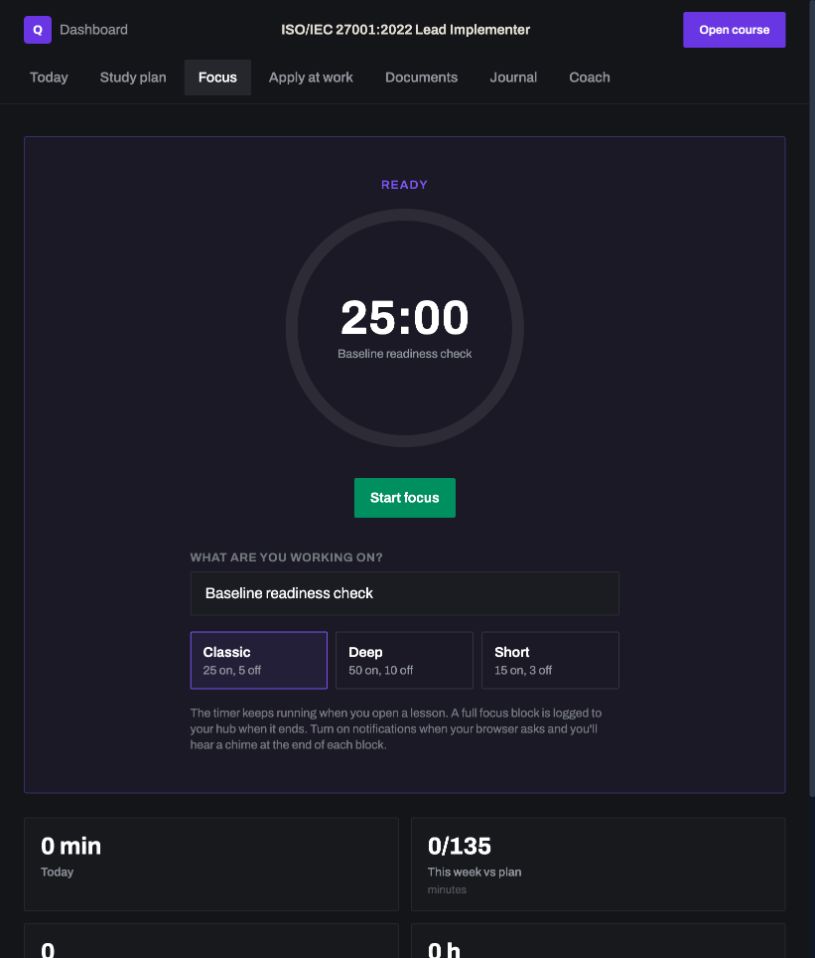
Focus timer: a real screen from ISO 27001 Lead Implementer

Focus timer · 25 minutes, no tab-hopping

One click starts a focused session, and it follows you from lesson to lesson. Short sessions are how busy people finish.

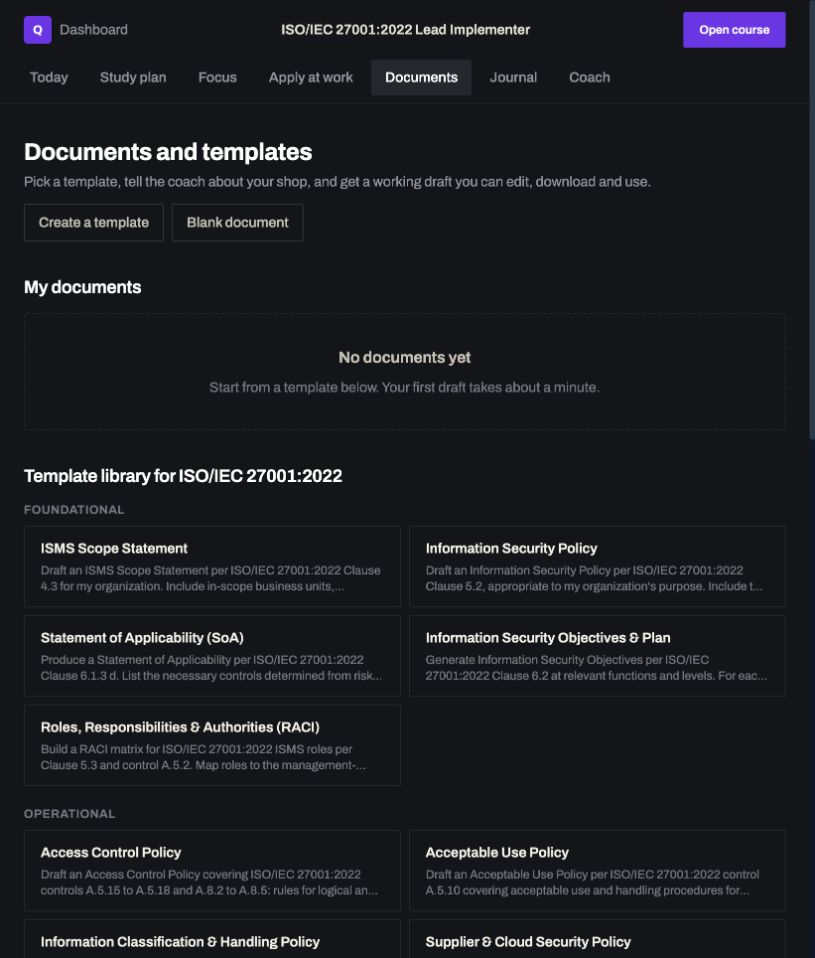
Course Hub: a real screen from ISO 27001 Lead Implementer

Course Hub · ISMS documents drafted with you

Pick a template, give Coach Q your facts, get a working draft you edit and keep: ISMS scope statement, risk register and treatment plan, Statement of Applicability, internal audit programme.

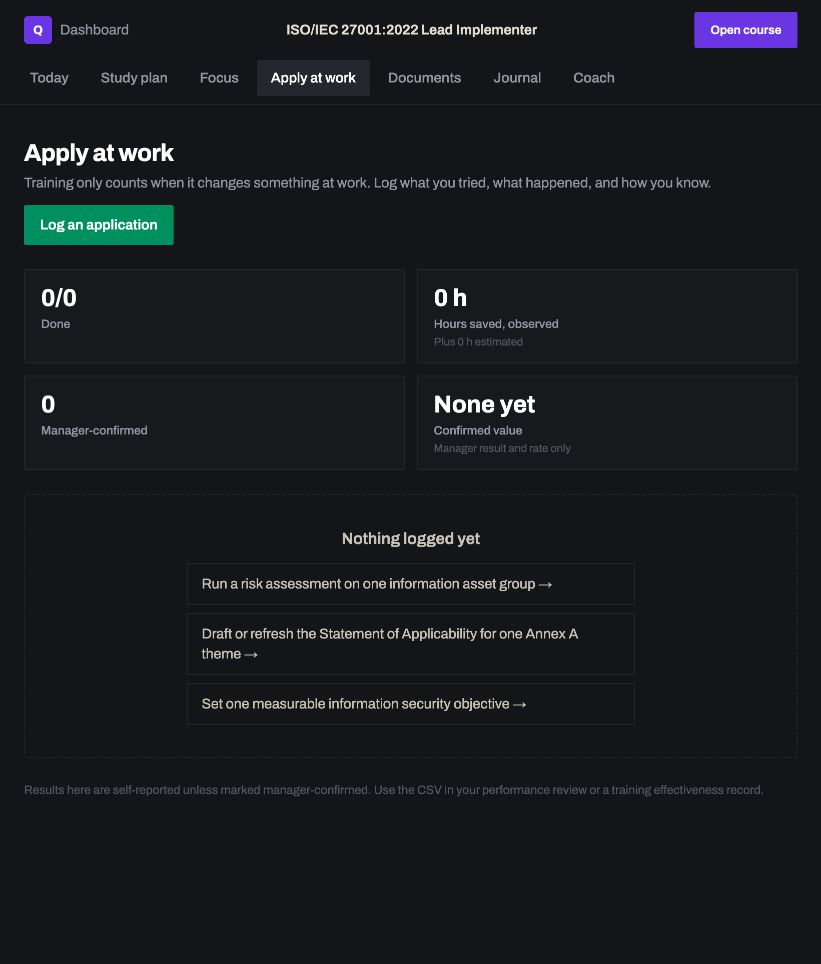
Apply at work: a real screen from ISO 27001 Lead Implementer

Apply at work · Proof your boss can see

Log what you tried, what happened and how you know. Record your manager's sign-off with their name and date, and export the log for your performance review.

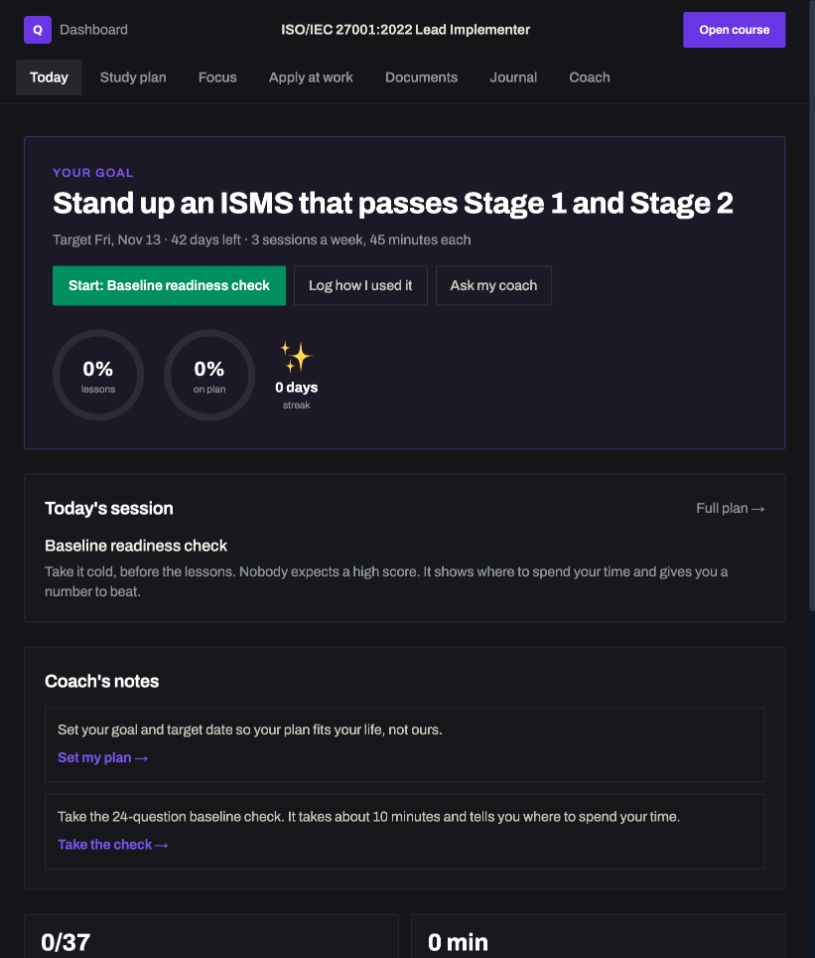
Today view: a real screen from ISO 27001 Lead Implementer

Today view · One look and you know what's next

Your goal, days left, lessons done, your streak and today's session.

Built around you

Give the study plan your goal date and it sizes each session to your week. Coach Q works on the facts you bring from your own job, so the examples are yours, not a textbook's.

Hands-on, not hours of video

Lessons are built around calls you make: read the record, sort the evidence, catch the mistake. Checks and labs score you on the spot, and your first win comes in the first few minutes of lesson 1.

Stays with you. Stays current.

Coach Q doesn't leave when you finish. It comes with your course, no subscription and no renewal fee, so it's there for the next customer questionnaire, and the next audit. When the rules behind this course change, we update the lessons and the coach's setup, and we move the coach to newer AI models as we test them.

What you walk out with

You don't just learn the clauses. You prepare the ISMS.

Context, interested parties and scope

Your issues, who has a stake and what they require, and a scope statement that covers what your customer actually cares about.

A risk method and treatment plan

Criteria and scales that give the same answer twice, risks identified across confidentiality, integrity and availability, and a plan the risk owners sign.

A Statement of Applicability

Necessary controls from your risk treatment, a justification and status for each, and a reason for every Annex A control you exclude.

A control set across all four themes

Policy framework, access reviews, supplier clauses, incident response, secure disposal, backup with restore testing and more.

An internal audit programme and corrective action log

Weighted to your riskiest processes, with an impartiality plan so nobody audits their own work.

A management review and readiness check

A review pack mapped to every required input, then a self-assessment against what a Stage 1 auditor reviews.

Inside the course

The course, step by step.

About 9 hours, self-paced, in short sessions that fit your week.

The ISMS Foundation

Clauses 4 and 5: context, scope, leadership, policy, roles, and the 2013-to-2022 transition. 5 lessons.

Risk, the Engine of the Standard

Clause 6.1: risk assessment methodology, identifying risk by C-I-A, analysis and evaluation, treatment and control selection, and the Statement of Applicability. 5 lessons.

Planning, Support, and Operation

Clauses 6.2, 6.3, 7, and 8: objectives, planning change, resources, competence, awareness, communication, documented information, and operational control. 5 lessons.

Organizational Controls (Annex A.5)

All 37 organizational controls in Annex A.5: policies, roles, threat intelligence, asset management, classification, access control, supplier security, incident management, continuity, and legal and privacy compliance. 8 lessons.

People and Physical Controls (Annex A.6 and A.7)

The 8 people controls (A.6) and 14 physical controls (A.7): screening, awareness, disciplinary process, reporting events, physical entry, environmental protection, equipment security, and secure disposal. 4 lessons.

Technological Controls (Annex A.8)

All 34 technological controls in Annex A.8: endpoints, privileged access, authentication, vulnerability and configuration management, backup and deletion, logging and monitoring, cryptography, and secure development. 5 lessons.

Performance, Audit, and Certification

Clauses 9 and 10 plus the certification journey: monitoring and measurement, internal audit, management review, nonconformity and corrective action, and the Stage 1 and Stage 2 audits. 5 lessons.

The itemized list

Everything you get.

Each priced line shows what a comparable item costs from another provider, with the source, so you can check it yourself. The included lines are what get the course finished. Checked October 12, 2026.

ISO 27001 Lead Implementer · itemAdding up: $2,770
01

The ISO 27001 Lead Implementer course

$2,770

Clauses 4 to 10 and all 93 Annex A controls in four themes, in the order you'd actually build an ISMS: context and scope, risk, the Statement of Applicability, controls, internal audit, management review and the certification audit. 74 real-world scenarios with explained answers and an AI checkpoint in every lesson.

COMPARABLE · IT Governance USA, Certified ISO 27001:2022 ISMS Lead Implementer Training Course, 3 days, instructor-led live online, exam included (us.grcsolutions.io, Oct 2026): $2,770

02

Course Hub with AI-drafted ISMS documents

Included

An ISMS scope statement, a risk register and treatment plan, a Statement of Applicability and an internal audit programme. Coach Q drafts each from your facts, you edit, save and download.

INCLUDED · adds nothing to the total

03

Coach Q, your expert in your pocket

Included

Ask the question you'd ask an auditor, any hour. It points you to the clause, the control and the evidence, and marks what's missing. It proposes, you decide. Comes with your course. No subscription or renewal fee. It stays with you after the course, and we keep its setup current when the rules change.

INCLUDED · adds nothing to the total

04

A Stage 1 readiness check

Included

A management review pack mapped to every required input, then a self-assessment against the documents a Stage 1 auditor reviews, with mock auditor questions.

INCLUDED · adds nothing to the total

05

Study plan, your personal trainer

Included

Built around your goal date and your week. It shows each day whether you're on plan and what today's session is.

INCLUDED · adds nothing to the total

06

Focus timer

Included

25-minute focused sessions that carry from lesson to lesson.

INCLUDED · adds nothing to the total

07

Apply at work log

Included

What you changed at work, with your manager's sign-off recorded, exportable for your review.

INCLUDED · adds nothing to the total

08

A certificate of completion anyone can verify

Included

Finish every lesson to earn it. It shows your name, the course and the date, and anyone can confirm it online. There's no final exam, and it isn't a PECB Lead Implementer credential or one from any other certification body.

INCLUDED · adds nothing to the total

09

Lessons for life

Included

Come back whenever the job needs it. Your access doesn't expire. We keep the lessons current for the edition this course teaches.

INCLUDED · adds nothing to the total

Priced elsewhere, piece by piece$2,770
Your price$395

One person, one time. $2,375 less than buying the comparable pieces.

People
1
Enroll for $395 →

5 or more people get 10% off every seat. Secure checkout by Stripe. 3-day refund.

Compare before you choose

Three ways to learn this. Here's the honest comparison.

Including the rows where a class wins.

What you pay
$395, once
$2,770 at IT Governance USA
Free or a monthly plan
Time away from work
No full days. About 9 hours at your pace
3 days, instructor-led online
None
Live instructor
No. Lessons by a registrar auditor, plus Coach Q
Yes
No
Lead Implementer exam and credential
No. A certificate of completion, no exam
Yes. The exam is included in the price
No
Documents for your own ISMS
Scope, risk method, SoA, controls, audit programme and management review, prepared lesson by lesson
Not listed on their page
It drafts. Checking it against your risks is on you
Help after the course
Coach Q and the lessons, for life. No renewal fee
Materials and guidance after the course
It explains. It won't grade you or vouch for you

ChatGPT will explain the clause. It will not grade you, and it will not vouch for you.

Prices are published list prices, checked October 12, 2026: IT Governance USA, Certified ISO 27001:2022 ISMS Lead Implementer Training Course.

Try before you buy

Try it before you pay. Change your mind after.

Before you pay

Lesson 1 is free.

The real first lesson, with the exercises and Coach Q. Your first win comes in the first few minutes. Judge it yourself.

Try lesson 1 free ↑

After you buy

3 days to change your mind.

Email will@qmslearning.com within 3 days of purchase for a refund. A refund ends access to the course. Refund policy

Company pays

Send it to your manager.

We wrote the email for you. Job training is generally a deductible business expense for the company, so check with your accountant. Need a quote or a PO? Email will@qmslearning.com.

Send this to my manager →

Questions

Straight answers.

Is this a PECB Lead Implementer certification?

No. It's called Lead Implementer because it covers the implementer's job end to end, from scope to the certification audit. It isn't a PECB Lead Implementer certification or one from any other certification body, and there's no exam. You earn a certificate of completion for your training record. If your employer or a customer requires a Lead Implementer credential, you'll need that body's exam.

Will my company be ISO 27001 certified when I finish?

No. A certification body certifies your organization after auditing your ISMS. The course teaches you to build the system and prepare for that audit. The certification body makes the decision.

How do I earn the certificate of completion?

Finish every lesson: the scenarios, the checks and the AI checkpoint. There's no final exam on this course. Your certificate shows your name, the course and the date, and anyone can confirm it at academy.qmslearning.com/verify.

Do I need the standard, and is the course current?

Keep a licensed copy of ISO/IEC 27001:2022 with Amendment 1 (February 2024) beside you. The lessons explain and cite the clauses and controls, including the climate change determination Amendment 1 added to clause 4.1, and the standard is the text your auditor audits against.

What does Coach Q do?

Coach Q, your private AI coach, comes with your course. No subscription or renewal fee. It's set up for this subject, works on the facts you give it and marks what's missing. It proposes, you decide: your risk owners accept the risk, and your organization reviews every document before use.

Has QMS Learning done this itself?

Yes. QMS Learning is ISO 27001 certified. The course was written by a third-party registrar auditor, clause by clause and control by control, around the evidence an auditor asks to see.

Why not just ask ChatGPT?

ChatGPT will explain the clause. It will not grade you, and it will not vouch for you. Ask it for a Statement of Applicability and it may mark every control implemented. This course trains you to check that every control matches a real risk and real evidence at your company.

How long do I keep access?

The lessons are yours for life, and Coach Q comes with your course and stays with you after you finish. There's no subscription or renewal fee.

Does the course keep up when the rules change?

Yes, for the edition it teaches. When the rules or guidance behind this course change, we update the lessons and the coach's setup, and you get the update at no extra charge. When a new edition replaces the standard, we point you to the transition training. Your conversations with Coach Q aren't used to train AI models.

Can my company pay?

Yes. Use a company card at checkout. Job training is generally a deductible business expense for the company, so check with your accountant. Need a quote or a PO first? Email will@qmslearning.com.

What if it isn't for me?

Try lesson 1 free before you pay. After you buy, email will@qmslearning.com within 3 days of purchase for a refund. A refund ends access to the course.

Training a team?

Pick how many people before you check out and pay once by card. Five or more people get 10% off every seat, applied at checkout. After checkout you add each person's name and email, and each of them gets their own login, private AI coach, study plan and certificate. More than 50 people, or need an invoice instead? Email will@qmslearning.com for a quote.
Everything, one more time

Build the ISMS. Then let the auditor test it.

  • The ISO 27001 Lead Implementer course$2,770
  • Course Hub with AI-drafted ISMS documentsIncluded
  • Coach Q, your expert in your pocketIncluded
  • A Stage 1 readiness checkIncluded
  • Study plan, your personal trainerIncluded
  • Focus timerIncluded
  • Apply at work logIncluded
  • A certificate of completion anyone can verifyIncluded
  • Lessons for lifeIncluded

Priced elsewhere, piece by piece: $2,770

$395

Per person, one time. Lessons for life. Coach Q included, no renewal fee.

About 9 hours. That's 18 half-hour lunch breaks.

People
1
Enroll for $395 →

5 or more people get 10% off every seat. Secure checkout by Stripe. 3-day refund.

Not ready to buy? Try lesson 1 free.

A customer questionnaire asks if you are ISO 27001 certified. Audit the answer and build a business case a CEO can sign.