Cybersecurity and CUI training path · self-paced
Sort your CUI. Know when it's an export. Run security as a system an auditor can test.When the prime, the auditor or DDTC asks, answer with records, not reassurance.AI can draft a security plan in an hour. Be the one who can prove it's true.
Sort FCI from CUI and post a NIST 800-171 score your evidence backs. Learn where ITAR draws the export line on drawings, people and shipments, then build an ISO 27001 information security system an auditor can test.
For IT, security and compliance leads at defense suppliers that handle CUI.
- 4 live courses, in order
- 3 more on the way
- Step 1: about 7.5 hours
- Coach Q in every course
Do we have to redo everything for NIST 800-171 Rev 3?
No. The CMMC rule still points at Rev 2. Spend the time on an honest self-assessment and a score you can stand behind.
Sound familiar?
If you handle security or compliance at a defense supplier, you've heard these.
Our prime wants our SPRS score, and I'm not sure we can back it up.
Then the score isn't ready to send. One failed objective fails the whole requirement, with no partial credit. The CMMC and NIST 800-171 course has you grade each objective the way an assessor does: examine, interview, test.
Engineering emails drawings to suppliers overseas. Is that a problem?
It can be. If a drawing is ITAR technical data, sending it to a foreign person is an export, and an NDA doesn't authorize it. The ITAR course shows where the line is, and the habit that keeps you behind it: stop, escalate, get the authorization in writing, then send.
A customer questionnaire asks if we're ISO 27001 certified.
Following the standard isn't the same as being certified, and buyers ask because they can't see inside your operation. The ISO 27001 course shows what the certificate proves, then has you draft the scope, risk assessment and Statement of Applicability a Stage 1 auditor looks at.
IT says we're secure. I can't tell what that means.
Secure is a feeling. An assessor wants dated records that show a control running over time: access reviews, log reviews, patch records. The CMMC and NIST 800-171 course explains each control in quality terms, so you know what to ask IT for.
What it does for you
Be the one they bring the CUI questions to.
The one with the real answer
When a prime asks for your score or engineering asks if a drawing can go, you'll know the rule, where the evidence is and who has to sign. That's the person a company trusts with its name.
Work you can show, not just a certificate
You leave with drafts for your own company, from a scoping worksheet to a Technology Control Plan, plus an Apply at work log that records what you did, with your manager's name and the date.
A stronger case for a bigger role
Nobody can promise you a raise or a title. What you can bring to that conversation is the work: a score you can defend, an export question raised before anything went out, a system an auditor can test.
No course can promise you a raise or a title. What you'll have is the skill, the work to show for it and a certificate anyone can verify. That's what those conversations run on.
Why it matters
Every security answer you send is a claim someone can check.
In June 2026, defense contractor LOGZONE agreed to pay $507,144 to resolve False Claims Act allegations; the issues were identified when DCMA assessed its NIST SP 800-171 controls and scored it -170, on a range of -203 to 110.
Source: U.S. Department of Justice, press release, June 18, 2026
The SPRS affirmation is a factual claim to the government, made by a senior official every year. CMMC Phase 2 was suspended on July 13, 2026, but NIST 800-171, the SPRS score, the annual affirmation and DFARS 252.204-7012 all still apply.
Your score is one call among several. Showing ITAR technical data to a foreign person is an export, even inside your own building, and it needs authorization first. A buyer can check an ISO 27001 claim against the certificate. Each call carries your company's name.
The full path
Start with CUI, then exports, then the whole system.
Start with CUI, because sorting it sets your level and your scope, then ITAR, since ITAR technical data under a DoD contract is generally CUI too, then ISO 27001 to run it all as one system. Each course stands alone.
-
Step 1 · Protect CUI and back up your score
CMMC & NIST 800-171
Sort FCI from CUI, read the clauses your contracts carry and draw the smallest boundary that holds. Then grade all 320 objectives the way an assessor does, write the SSP and post a score your evidence backs.
You walk out with an FCI and CUI data inventory, your boundary drawn on a scoping worksheet, an SSP started and an SPRS score worksheet you can stand behind.
- About 7.5 hours
- Certificate anyone can verify
- Lesson 1 free
See what you get →The course page shows everything included, then the price.
-
Step 2 · Know when it's an export
ITAR Compliance
Classify parts by USML paragraph, spot a release in an email, a screen share or a plant tour, and match each export to a license, agreement or exemption. Then build a Technology Control Plan that matches the floor.
You walk out with a classification worksheet for your own parts, a Technology Control Plan and deemed export procedure for your shop, and a dated 90-day roadmap.
- About 10 hours
- Final exam
- Certificate anyone can verify
- Lesson 1 free
See what you get →The course page shows everything included, then the price.
-
Step 3 · Run security as a system
ISO 27001 Information Security
Scope an ISMS that follows the data, build a risk method that gives the same answer twice, and write a Statement of Applicability from your own risk treatment. Then audit it yourself before Stage 1 and Stage 2.
You walk out with a scope statement, risk method and register, a Statement of Applicability, an internal audit program and a management review pack for your own ISMS.
- About 9 hours
- Certificate anyone can verify
- Lesson 1 free
See what you get →The course page shows everything included, then the price.
Step 4 · Protect information when working with AI
Protect Information When Working with AI
Classify what you hold under a written policy, cut an input down to what the question needs, check unusual requests through a route you already know, treat text inside documents as data, keep a tool's access small and report a slip fast. Ends with a human-reviewed final case study and a 30-question final exam.
You walk out with an information handling table, a minimum input and route record, a request verification record, an outside-content note, a tool permission card and a first exposure report, plus an assessed certificate of completion.
- About 4.5 hours
- Final exam
- Human-reviewed case
- Lesson 1 free
See what you get →See the complete offer, then the price.
On the way in this path
More courses for this path are on the way, each with its own waitlist, so you can tell us which one you need first.
-
On the way
CUI Handling on the Shop Floor and in the Office
Find where CUI leaks: drawings, email, travelers and shared drives.
-
On the way
Incident Response for Small Defense Suppliers
Work the 72-hour reporting clock before you ever need it.
-
On the way
Cybersecurity Awareness
Spot phishing and protect company data. For every employee.
Not like training used to be
Short, hands-on, built around you. And the coach stays.
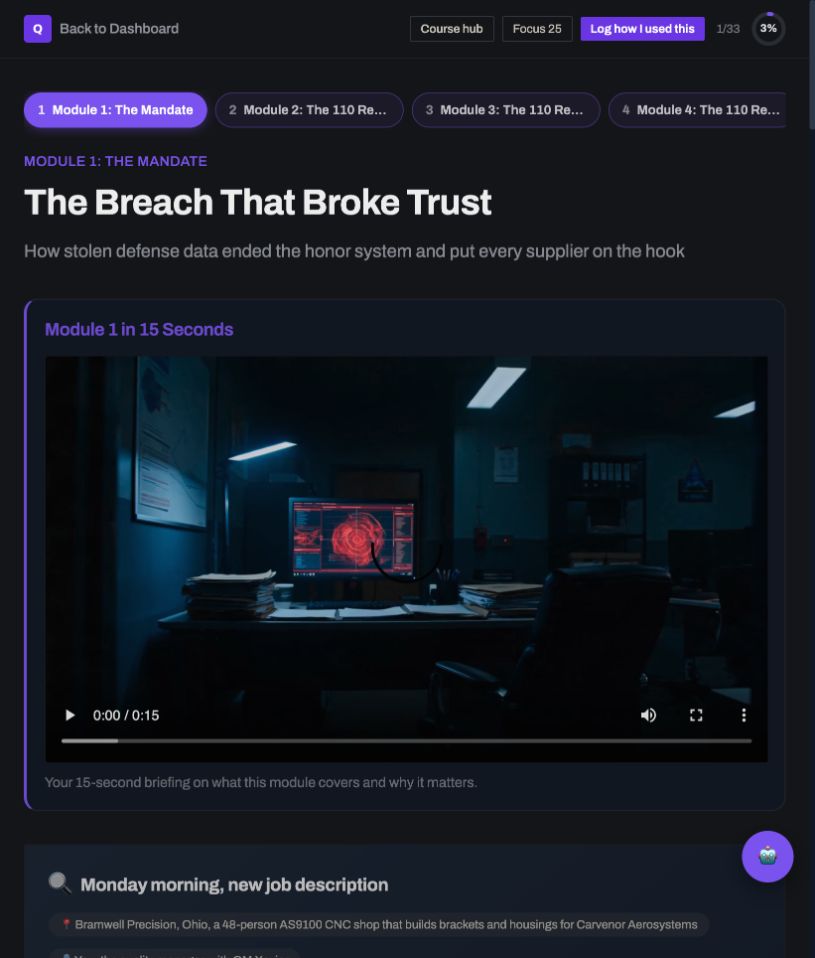
Training used to mean days in a classroom or hours of video. Here are real screens from this path: short sessions where you make the call, a plan that fits your week, and an expert in your pocket in every course.
Coach Q · from CMMC & NIST 800-171
No. The CMMC program rule, 32 CFR 170.2, still incorporates Revision 2. Rev 3 exists, but it isn't what your contracts or an assessment point at today.
Your time is better spent on the Rev 2 work that counts now: an honest self-assessment, the evidence behind each requirement, and a score in SPRS you can stand behind. Keep someone assigned to watch for any change to the rule.
Coaching, not decisions. You make the call. Comes with every course, no renewal fee.
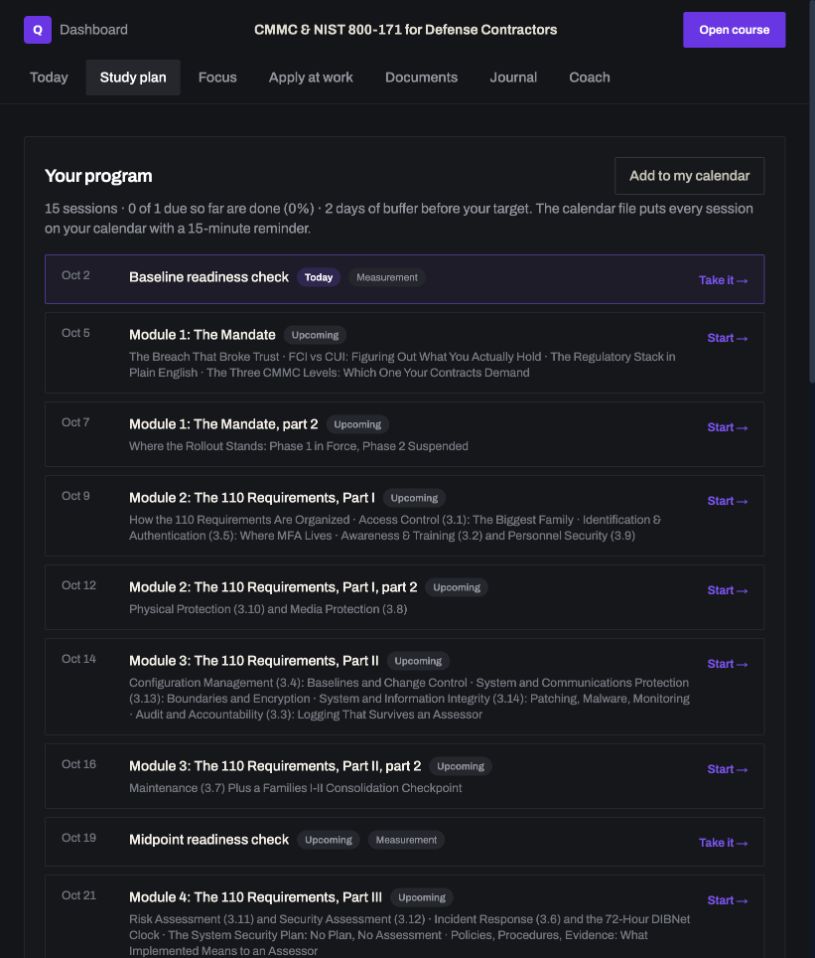
Study plan · Your personal trainer
Tell it your goal date. It builds sessions around your week and shows each day whether you're on plan, so the course actually gets finished.
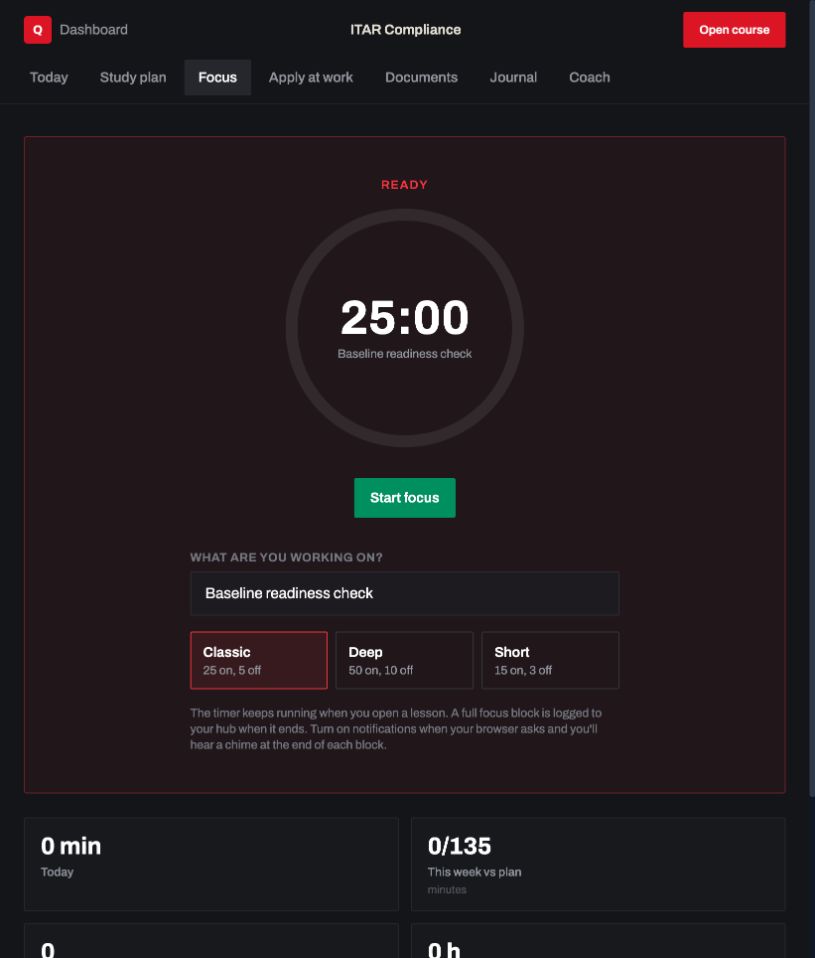
Focus timer · 25 minutes, no tab-hopping
One click starts a focused session, and it follows you from lesson to lesson. Short sessions are how busy people finish.
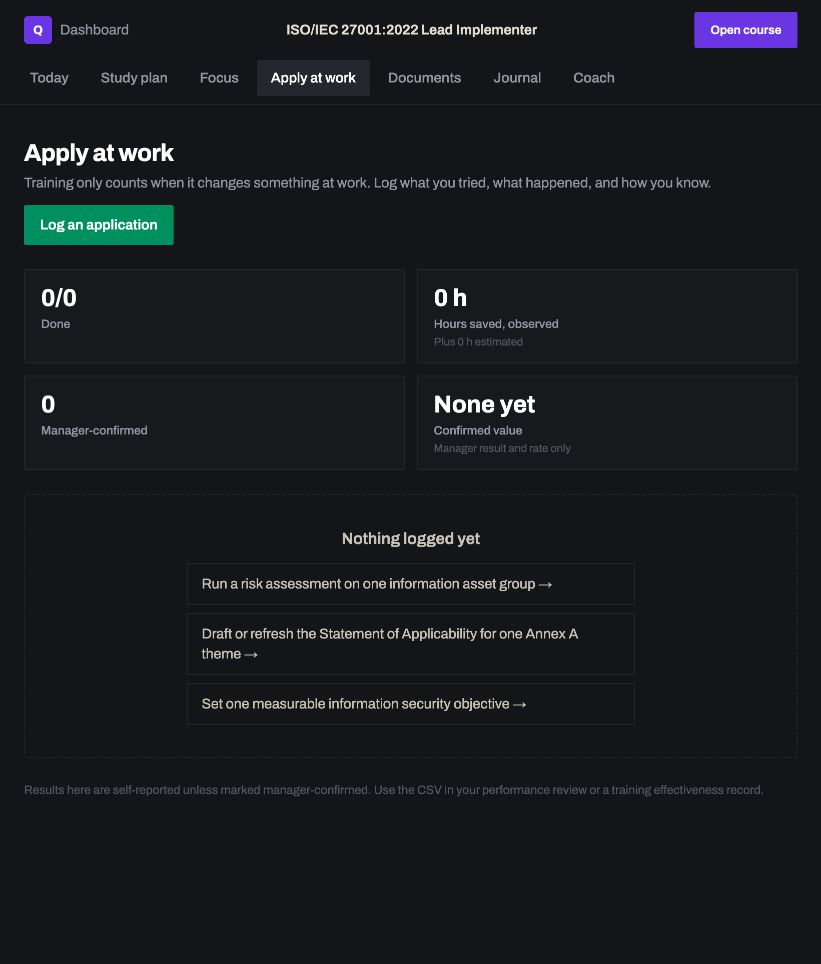
Apply at work · Proof your boss can see
Log what you tried, what happened and how you know. Record your manager's sign-off with their name and date, and export the log for your performance review.
Built around you
Give the study plan your goal date and it sizes each session to your week. Coach Q works on the facts you bring from your own job, never CUI or technical data, so the examples are yours, not a textbook's.
Hands-on, not hours of video
Lessons are built around calls you make: read the record, sort the evidence, catch the mistake. Checks and labs score you on the spot, and your first win comes in the first few minutes of lesson 1.
Stays with you. Stays current.
Coach Q doesn't leave when you finish. It comes with your course, no subscription and no renewal fee, so it's there for next year's affirmation and the next customer questionnaire, kept general and never with CUI or technical data. When the rules behind this course change, we update the lessons and the coach's setup, and we move the coach to newer AI models as we test them.
What you walk out with
Working documents for your own company, not notes.
In Course Hub you pick a template and give Coach Q facts you're allowed to share, never CUI or technical data. It drafts a first version. You edit it, and it's yours to keep and use.
CMMC & NIST 800-171
- FCI/CUI Data Inventory + Flow MapDraft with Coach Q
- Scoping Worksheet + Asset CategorizationDraft with Coach Q
- System Security Plan (SSP) BuilderDraft with Coach Q
- SPRS Score Worksheet (DoD Assessment Methodology)Draft with Coach Q
ITAR Compliance
- Jurisdiction & Classification Determination WorksheetDraft with Coach Q
- Technology Control Plan (TCP)Draft with Coach Q
- Deemed Export ProcedureDraft with Coach Q
ISO 27001 Information Security
- ISMS Scope StatementDraft with Coach Q
- Statement of Applicability (SoA)Draft with Coach Q
Who built it
Built from the auditor's chair and the supplier's side.
Will Trikha
Founder and CEO, QMS Learning · Third-party registrar auditor
Will Trikha is a third-party registrar auditor with more than 20 years in aerospace and quality. He wrote these courses around the evidence an auditor asks to see, because a score, an export decision or a security claim is only as good as the record behind it.
He's COO of PTX Defense, an AS9100D-certified aerospace manufacturer, so he lives with these requirements from the supplier side too. He founded QMS Leader, a consulting firm that implements quality management systems for manufacturers. His own company, QMS Learning, earned ISO 27001 certification in 2026.
Check us before you pay
- Take lesson 1 free. The real first lesson of any course on the path, with Coach Q. No card.
- Look Will up. His LinkedIn profile lists the work behind the courses.
- Check a certificate. Every certificate can be confirmed at academy.qmslearning.com/verify.
- Keep your exit. 3 days after you buy a course to ask for a refund.
Try before you buy
Try it before you pay. Change your mind after.
Before you pay
Lesson 1 is free.
Every live course on the path has a free first lesson, with the exercises and Coach Q. Start with step 1 and judge it yourself.
Try lesson 1 free ↑After you buy
3 days to change your mind.
Email will@qmslearning.com within 3 days of buying a course for a refund. A refund ends access to that course. Refund policy
Company pays
Send it to your manager.
We wrote the email for you, with each course on the path and a link to what it includes. Need a quote or a PO? Email will@qmslearning.com.
Send this to my manager →Questions
Straight answers.
Do I have to take them all?
No. Each course stands on its own, and lesson 1 is free on each one. The path is the order we'd take them in. Start wherever your job needs you most.
Which one should I start with?
If a prime is asking for your SPRS score, start with CMMC and NIST 800-171. If drawings go to foreign suppliers or a new hire isn't a U.S. person, start with ITAR. If customers are asking about ISO 27001, start with the ISO 27001 course.
What's the status of CMMC?
CMMC Phase 2 was suspended on July 13, 2026. NIST 800-171, SPRS scores, annual affirmations and DFARS 252.204-7012 still apply, so the work in the CMMC and NIST 800-171 course still counts.
Is this an accredited certification?
No. Each course ends with a certificate from QMS Learning that anyone can check at academy.qmslearning.com/verify, and the ITAR course also has a final exam. It isn't an accredited ISO 27001 Lead Implementer credential or a CMMC assessor credential, and it doesn't certify your company.
Can I put our real data into Coach Q?
Not CUI, and not export-controlled technical data, in Coach Q or any other AI tool. Describe the situation in general terms or work the course's fictional cases. The coach marks what's missing and never affirms a score, accepts a risk or decides whether something is an export. Named people at your company do.
Training a team?
Open any course on the path and pick how many people before you check out. Five or more people get 10% off every seat, applied at checkout. Each person gets their own login, private coach, study plan and certificate. More than 50 people, or need an invoice instead? Email will@qmslearning.com for a quote.
How long do I keep access?
The lessons are yours for life, and Coach Q comes with your course and stays with you after you finish. There's no subscription or renewal fee.
Does the course keep up when the rules change?
Yes, for the edition it teaches. When the rules or guidance behind this course change, we update the lessons and the coach's setup, and you get the update at no extra charge. When a new edition replaces the standard, we point you to the transition training. Your conversations with Coach Q aren't used to train AI models.
The Cybersecurity and CUI path
Sort your CUI first. Lesson 1 of CMMC and NIST 800-171 is free.
- Step 1: CMMC & NIST 800-171About 7.5 hours
- Step 2: ITAR ComplianceAbout 10 hours
- Step 3: ISO 27001 Information SecurityAbout 9 hours
- Step 4: Protect Information When Working with AIAbout 4.5 hours
Lessons for life. Coach Q comes with every course, no renewal fee.
Ready to buy? Pick a course from the path. Each course page shows everything included, then the price.